PDPL, Explained: What Saudi Merchants Need to Know
PDPL is in full force. Every merchant who prints a receipt is now a regulated data controller. Here's the plain-language guide — fines, deadlines, and the fastest path to compliance.
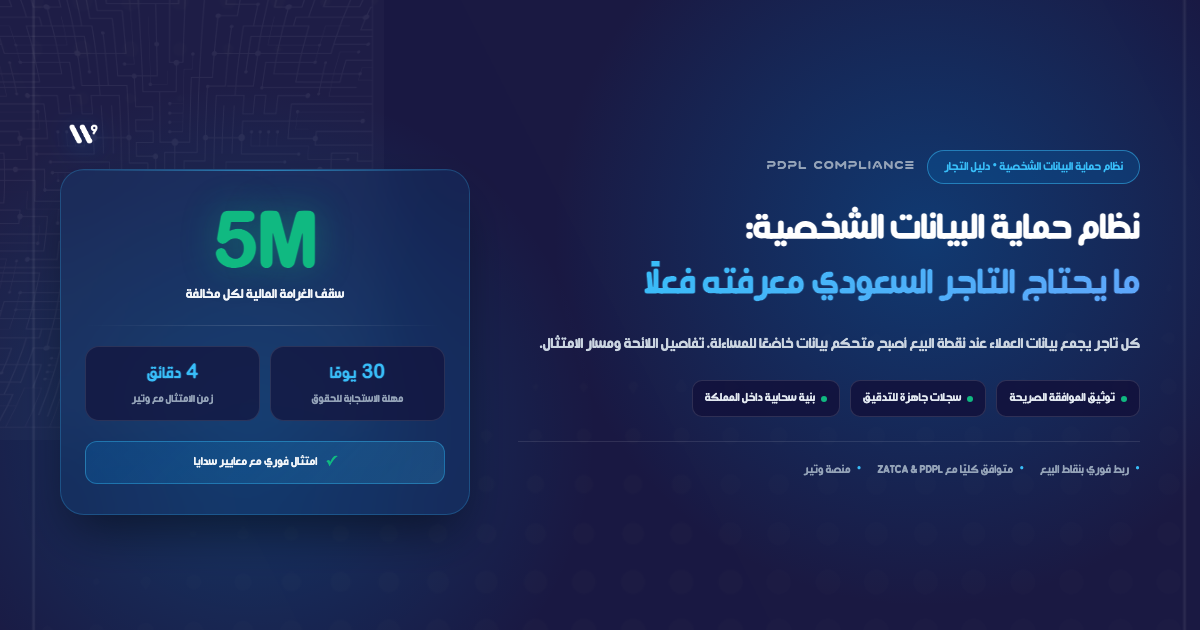
PDPL is live, and it applies to you
Saudi Arabia's Personal Data Protection Law (PDPL) came into full enforcement in September 2024. The grace period has closed. SDAIA, the Saudi Data and AI Authority, issued 48 enforcement decisions in the first year, with fines reaching SAR 5,000,000 per violation. Repeat offenders pay double.
If you trade in the Kingdom and collect any customer information, a phone number at the till, an email for a loyalty program, a name on a warranty card, you are a data controller under the law. That status carries obligations you cannot set aside.
What PDPL actually requires
Stripped back, PDPL says one thing: if you hold someone's personal data, you must handle it responsibly. In practice, that means:
Collect data lawfully, with consent you can prove.
Be clear about why you are collecting it, and use it only for that purpose.
Keep only what you need, for only as long as you need it.
Protect it with reasonable security measures.
Respond to customers who ask to access, correct, or delete their data.
Obtain authorization before moving personal data outside Saudi Arabia.
The fines are real
This is not a framework without consequences. The maximum penalty is SAR 5M per violation, rising to SAR 10M for repeat offenders. Mishandling sensitive personal data, covering health, biometrics, and religion, carries a fine of up to SAR 3M. Intentional disclosure can bring up to two years in prison.
Cross-border transfer without authorization carries a separate SAR 1M fine plus up to a year in prison. That matters, because most cloud services, including Stripe, Shopify, Google Analytics, and many POS platforms, transfer data outside Saudi Arabia by default.
The merchants under the most pressure
Food and beverage, retail, and pharmacy chains face the sharpest exposure, simply because they generate more customer data per transaction than anyone else. Every thermal receipt printed with a phone number, every loyalty signup, every returned item is a data point that PDPL governs. In most cases there is no consent log, no retention policy, and no audit trail behind any of it. That is the easiest kind of violation to uncover.
The fastest path to compliance
You have two routes. The first: hire a data protection consultant, draft policies, train staff, rebuild your POS workflow, audit every vendor, and budget SAR 50k to 150k a year to keep it all current. The second: run on infrastructure that is compliant by default.
Wateer is the second route. Every receipt we issue is created, stored, and transferred under SDAIA's implementing regulations. Consent logs, retention policies, and rights requests are handled automatically. You integrate in minutes and inherit the full compliance layer.
PDPL is here to stay. The question is not whether to comply, but how much friction you are willing to absorb on the way there.
Sources & References
Related reading
Want to see Wateer on your system?
Talk to Sales